OneDrive and SharePoint Connectors
The C3 Agentic AI Platform has a built-in connector for integrating with OneDrive and SharePoint.
Run the JavaScript code on this page in the C3 AI Console of your application. The JSON files go in your package metadata.
Authentication options for connecting to OneDrive or SharePoint
The C3 Agentic AI Platform supports two authentication flows for connecting to Microsoft OneDrive or SharePoint through the Microsoft Graph APIs:
- Delegated authentication (authorization code flow)
- App-based authentication (client credentials flow)
For more details about the two options, see the Microsoft documentation:
Delegated authentication (authorization code flow)
Use this option when the connector acts on behalf of a user. This flow requires interactive user sign-in and consent, and returns both access and refresh tokens. Access is limited to the permissions of the signed-in user. Use this flow when the application needs to access a user's personal OneDrive or SharePoint files.
- Requires: User sign-in and an authorization code
- Token type: Access token and refresh token
- Suitable for: User-driven access, personal file operations, and user-scoped SharePoint access
To connect to OneDrive or SharePoint from your application:
- Create an OAuth 2.0 client in Microsoft Entra ID (formerly Azure Active Directory, AAD).
- Add a FileSourceSystem on which to set credentials.
- Configure the MsGraphCredentials that authorize the connection to OneDrive or SharePoint.
- Set a file system mount that points to the directory you want.
Create an OAuth 2.0 client
In the Azure Portal, go to App registrations and add a new registration.
Under Redirect URI (optional), select Web and enter https://c3.ai for the URI.
Under Implicit grant and hybrid flows, select both Access tokens and ID tokens.
Add a FileSourceSystem
Create a FileSourceSystem and set the following fields:
name: Unique identifier for the OneDrive or SharePoint instancerootUrlOverride: The root URL for the source system. For OneDrive, the root URL must contain at least the drive name. For SharePoint, the root URL must contain at least the site name.
For example, to access your documents folder in OneDrive, add the following OneDriveFileSource.json to the /metadata/FileSourceSystem directory of your package:
{
    "name": "EdmPersonalDocuments",
    "rootUrlOverride": "msgraph://documents/"
}
To access a specific SharePoint site, add the following SharePointFileSource.json to the /metadata/FileSourceSystem directory of your package. Replace the name with your own:
{
    "name": "SharePointSystem",
    "rootUrlOverride": "msgraph://ExampleSharePointSite/"
}Configure the credentials
Construct the authorization URL. This URL generates an authorization code to exchange for access and refresh tokens.
var client_id = "<CLIENT_ID>"
var redirect_uri = "<REDIRECT_URI>"

query = `client_id=${client_id}&scope=offline_access%20user.read%20files.read%20files.read.all%20files.readwrite%20files.readwrite.all&response_type=code&redirect_uri=${redirect_uri}`

//  If the app registration is single-tenant, run this after replacing the active directory ID:
var active_directory_id = "<ACTIVE_DIRECTORY_ID>"
url = Url.builder().scheme("https").host("login.microsoftonline.com").encodedPath(`/${active_directory_id}/oauth2/v2.0/authorize`).encodedQuery(query).build()

// If the app registration is multi-tenant, run this:
url = Url.builder().scheme("https").host("login.microsoftonline.com").encodedPath("/common/oauth2/v2.0/authorize").encodedQuery(query).build()

url.toString()
Open the generated authorization URL in a browser and complete the Microsoft sign-in and consent flow.
Some organizations do not let users grant delegated Microsoft Graph permissions. If your organization requires administrator approval, Microsoft shows a Need admin approval message instead of the consent screen. In that case, ask your Microsoft Entra ID administrator or IT team to approve the delegated Microsoft Graph permissions that the authorization URL requests. If you change the authorization URL to request other delegated scopes, your administrator must approve those scopes instead.
After authentication completes, copy the authorization code from the redirect URI in your browser's address bar. The redirect URI has the following format:
https://<REDIRECT_URI>/?code=<AUTH_CODE>&session_state=<SESSION_STATE>Copy only the value of the code query parameter, shown as <AUTH_CODE>. Then create an MsGraphCredentials instance and use the authorization code to get OAuth access and refresh tokens.
var auth_code = "<AUTH_CODE>"

var creds = MsGraphCredentials.make({
    // For OneDrive, no endpoint is required

    // If using a SharePoint site, uncomment the following line and change the value to the endpoint for your SharePoint tenant:
    // "endpoint": "c3e.sharepoint.com",
    "activeDirectoryId": "<ACTIVE_DIRECTORY_ID>",
    "accessKey": "<CLIENT_ID>",
    "secretKey": "<CLIENT_SECRET>"
})

//  If the app registration is single-tenant, run this after replacing the active directory ID:
res = creds.acquireTokenFromAuthorizationCode(auth_code, redirect_uri, "<ACTIVE_DIRECTORY_ID>")

// If the app registration is multi-tenant, run this:
res = creds.acquireTokenFromAuthorizationCode(auth_code, redirect_uri)

access_token = res['access_token']
refresh_token = res['refresh_token']
Finally, add the access and refresh tokens to the credentials and set them on the FileSourceSystem you created earlier.
creds = creds.withAccessToken(access_token).withRefreshToken(refresh_token)

// Replace "EdmPersonalDocuments" with the name of your FileSourceSystem (it may be "SharePointSystem" if connecting to SharePoint and you copied the example above)
FileSourceSystem.forName("EdmPersonalDocuments").setCredentials(creds)Set a file system mount pointing to the desired directory
For OneDrive, add mounts to access OneDrive directories and list files.
FileSystem.msgraph().setMount("EdmPersonalDocuments", "msgraph://documents/")

FileSystem.msgraph().listFiles("msgraph://documents/")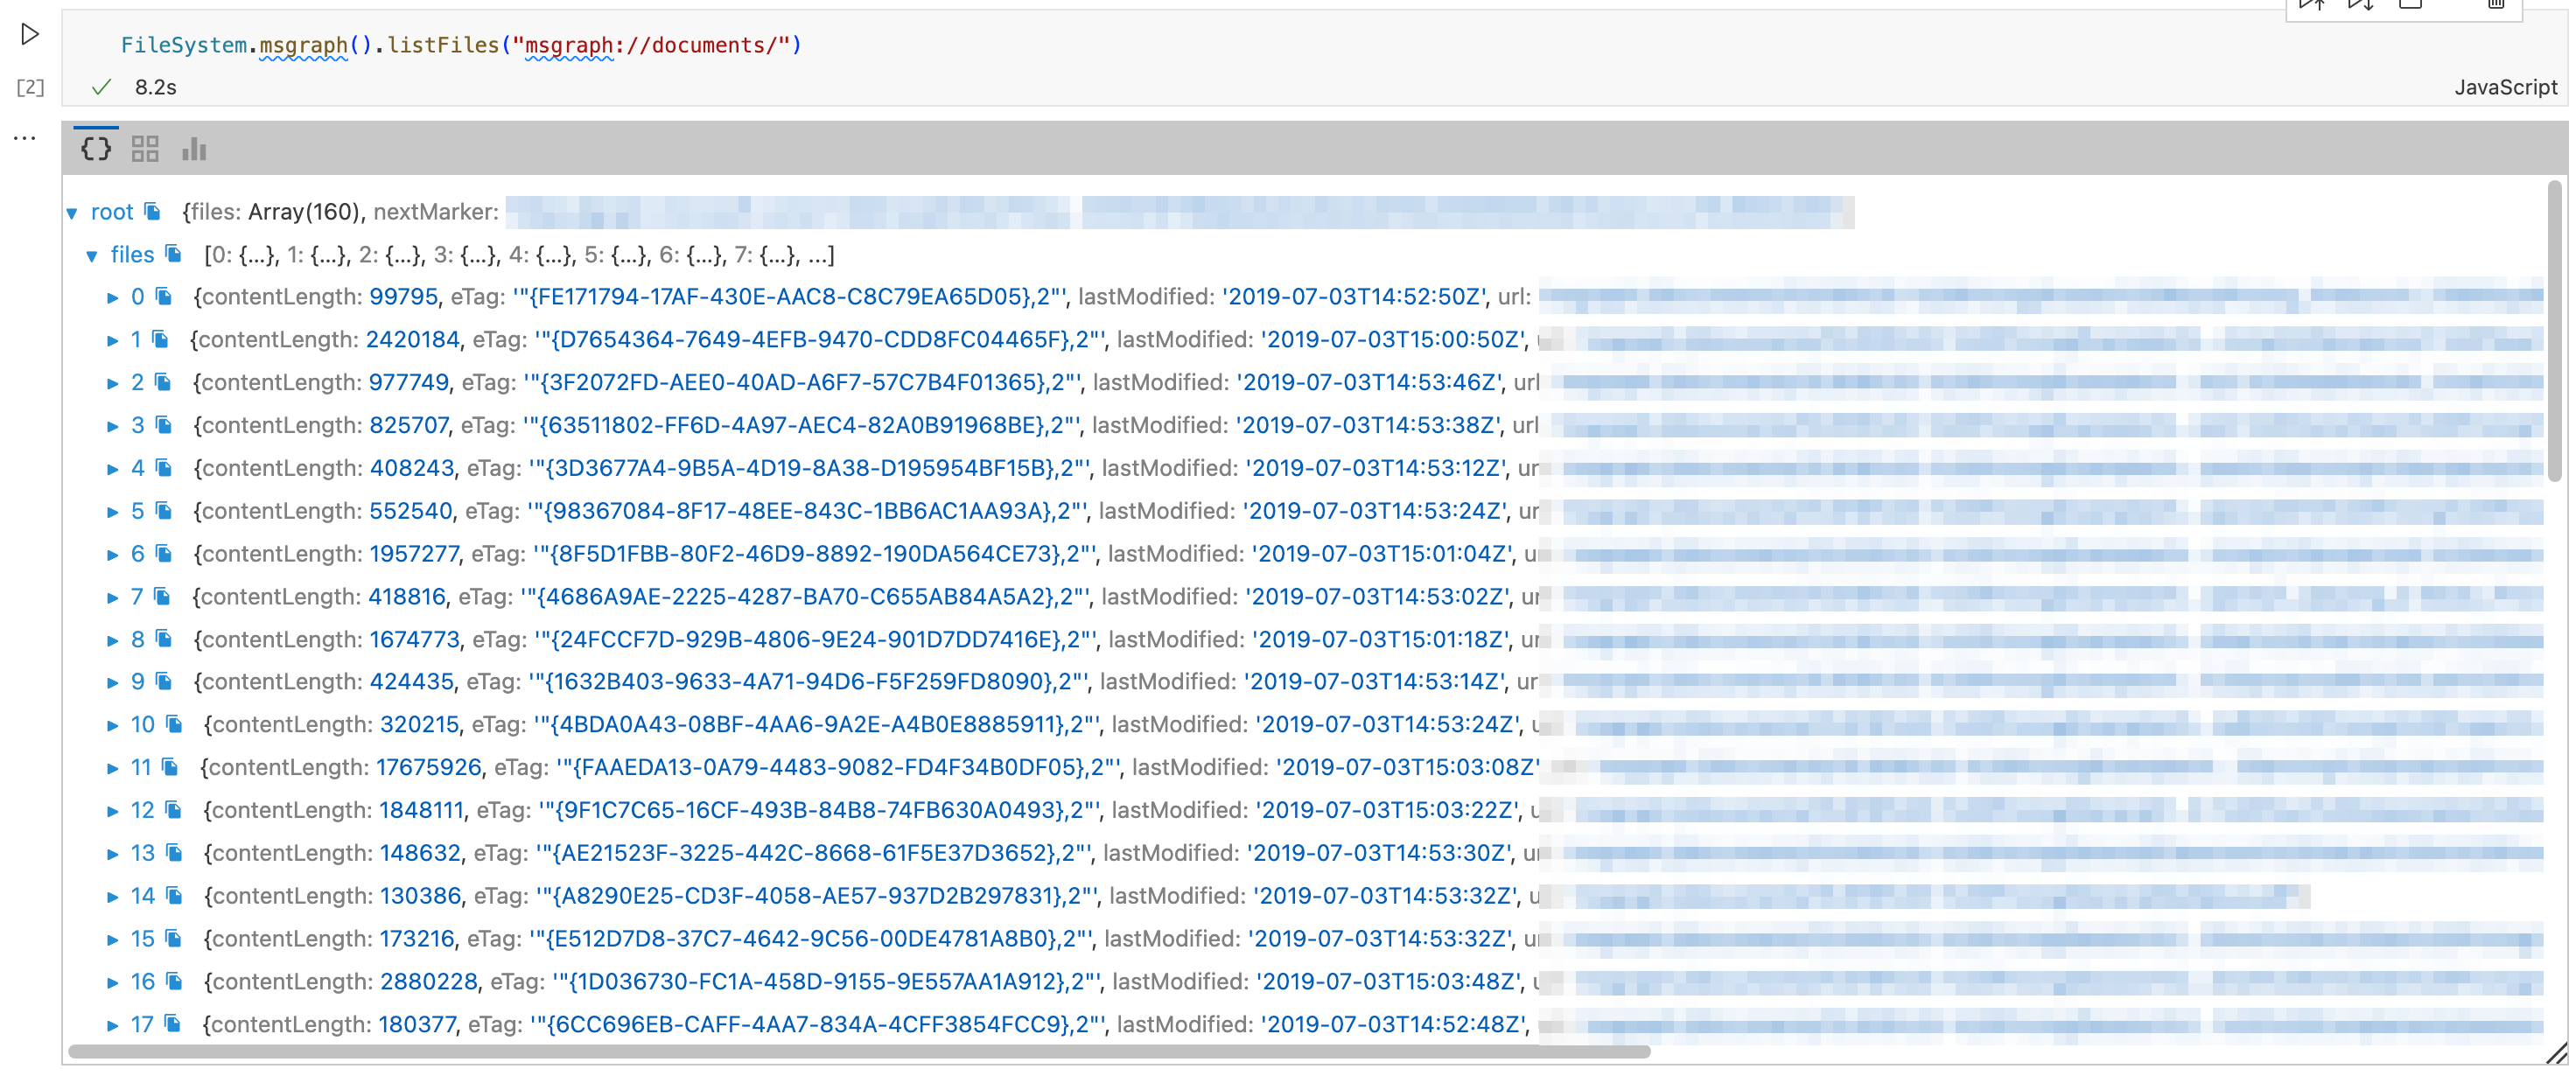
For SharePoint, mount to a specific drive (recommended) or to an entire site.
// Mount the documents drive of a site
FileSystem.msgraph().setMount("documentsmount", "msgraph://ExampleSharePointSite/Documents/")

// Mount an entire site - only do this if you are okay with giving access to all drives in the site
FileSystem.msgraph().setMount("sitemount", "msgraph://ExampleSharePointSite/")

// List files from the documents drive. Be sure to provide both the site and drive.
FileSystem.msgraph().listFiles("msgraph://ExampleSharePointSite/Documents/")App-based authentication (client credentials flow)
Use this option when the application accesses resources as itself, without user interaction. This flow uses a client ID and client secret to request an access token directly, and it does not issue a refresh token. Access to SharePoint sites usually needs admin consent. Personal OneDrive accounts are not supported.
- Requires: App registration with admin consent
- Token type: Access token only
- Suitable for: Background processes, service-level access, and tenant-wide SharePoint access
Use this flow to access files on SharePoint sites without signing in on behalf of a designated user. This flow cannot access personal OneDrives.
Create the OAuth client
In the Azure Portal, go to App registrations and add a new registration.
Under Redirect URI (optional), select Web and enter https://c3.ai for the URI.
Under Implicit grant and hybrid flows, select both Access tokens and ID tokens.
The client credentials grant flow requires admin consent for the app's permissions. To access files on all sites in your tenant, request the Files.Read.All and Files.ReadWrite.All permissions. To limit the app to some sites, request Sites.Selected instead. A tenant admin then configures which sites the app can access.
To request permissions, go to Manage > API permissions. Select Add a permission > Microsoft Graph > Application permissions, and then select the permissions you need. Select Add permissions and ask an admin for approval.
Add a FileSourceSystem (same as delegated user flow)
For example, create SharePointFileSource.json and add it to the /metadata/FileSourceSystem directory. The root URL must contain the site name, so replace ExampleSharePointSite with your site name.
{
    "name": "SharePointSystem",
    "rootUrlOverride": "msgraph://ExampleSharePointSite/"
}Configure credentials
var creds = MsGraphCredentials.make({
    "endpoint": "c3e.sharepoint.com",
    "accessKey": "<CLIENT_ID>",
    "secretKey": "<CLIENT_SECRET>",
    "activeDirectoryId": "<ACTIVE_DIRECTORY_ID>"
})
Set endpoint to the URL of the target SharePoint tenant, for example c3e.sharepoint.com.
After you replace the Active Directory ID, get an access token:
res = creds.acquireTokenWithClientCredentials("<ACTIVE_DIRECTORY_ID>")
access_token = res["access_token"]Add the access token to the credentials and set them on the FileSourceSystem
creds = creds.withAccessToken(access_token)

FileSourceSystem.forName("SharePointSystem").setCredentials(creds)
Then mount to a specific drive (recommended) or to an entire site.
Mount the documents drive of a site
Replace ExampleSharePointSite with your site name and Documents with your drive name.
FileSystem.msgraph().setMount("documentsmount", "msgraph://ExampleSharePointSite/Documents/")Mount an entire site
Replace ExampleSharePointSite with your site name.
FileSystem.msgraph().setMount("sitemount", "msgraph://ExampleSharePointSite/")You can now call file system operations. When you call an operation such as listFiles for SharePoint, provide both the site and the drive.
FileSystem.msgraph().listFiles("msgraph://ExampleSharePointSite/Documents/")Configure Microsoft sovereign cloud endpoints (optional)
Use this configuration only if your Microsoft 365 tenant runs in a supported Microsoft sovereign cloud environment.
Commercial Microsoft 365 deployments use the default Microsoft Graph and Microsoft Entra ID endpoints and need no extra endpoint configuration.
For supported sovereign cloud deployments, configure both of the following fields:
- Graph Endpoint: The Microsoft Graph API endpoint that the connector uses.
- Login Endpoint: The Microsoft Entra ID authentication endpoint that issues OAuth tokens.
In code, these are the graphEndpoint and loginEndpoint fields of MsGraphCredentials.
The connector derives the OAuth scope from the configured Graph Endpoint. Configure both endpoint values for the same sovereign cloud environment.
Supported endpoint values
| Microsoft environment | Graph Endpoint | Login Endpoint |
|---|---|---|
| Commercial (default) | https://graph.microsoft.com | https://login.microsoftonline.com/ |
| US Government L4 (GCC High) | https://graph.microsoft.us | https://login.microsoftonline.us/ |
| US Government L5 (DoD) | https://dod-graph.microsoft.us | https://login.microsoftonline.us/ |
Example
The following example shows the values for a SharePoint tenant in GCC High, as you enter them in the OneDrive/SharePoint connector form in Data Fusion. For the other fields of that form, see Authenticate File Sources.
Credential Name: SharePoint GCC High

Tenant ID: <tenant-id>
Client ID: <client-id>
Client Secret: ********

Endpoint: <placeholder>.sharepoint.com (only required for SharePoint)

Graph Endpoint:
https://graph.microsoft.us

Login Endpoint:
https://login.microsoftonline.us/
Both endpoint values must belong to the same Microsoft sovereign cloud environment. Endpoint values from different environments cause authentication failures.